Open source security infrastructure for AI agents.
Built for AI agents. Not humans, services, or workflows repurposed as agents. Identity, observability, and policy for the systems that are starting to act on your behalf.
The problem
AI agents are already making decisions, calling APIs, and accessing production data. They are doing so without identity, visibility, or accountability. One compromised or misaligned agent can silently exfiltrate data, escalate privileges, or delete critical systems, and most organizations will not notice until damage is done.
What we do
We build the open source security infrastructure that the agent economy was launched without. Ten tools, all Apache 2.0, all self-hostable. Identity, scanning, runtime control, adversarial testing, and pre-install trust verification for any AI agent your team or your vendors deploy.
AI agents should be powerful. They should never be unaccountable.
What we build
Ten open source tools. Each works standalone. Together they form the security infrastructure for AI agents.
AIM
Agent Identity Management
Cryptographic identity, MCP server attestation, trust scoring, capability-based access control, and an audit trail of every agent's actions.
OpenA2A CLI
One unified command surface across the OpenA2A ecosystem. Scan, protect, monitor, and review every AI surface from a single binary.
HackMyAgent
Security scanner, red team toolkit, OASB benchmarking, and runtime protection. 318 static checks across 73 categories, 29 NanoMind semantic checks, 164 adversarial payloads, auto fix with rollback.
Secretless AI
Keeps secrets out of AI context windows. In Claude Code a pre tool use hook blocks credential file reads. For Cursor, Copilot, and Windsurf it writes an instruction file that nothing enforces.
ai-trust
Pre install trust verification for AI packages. MCP servers, A2A agents, skills, AI tools, and LLMs checked against the OpenA2A Registry.
OASB
OpenA2A Security Benchmark
222 attack scenarios across 10 test categories, mapped to 15 MITRE ATLAS techniques. OASB-1 standard: 46 controls at 3 maturity levels.
Runtime Protection
Process, network, and filesystem monitoring with protocol aware detection for MCP, A2A, and OpenAI traffic. Run via opena2a-cli runtime.
Browser Guard
Chrome extension that detects and monitors browser-based AI agents. Layered detection, delegation engine, and session timeline.
DVAA
Damn Vulnerable AI Agent
21 intentionally vulnerable agents across 12 vulnerability categories, 86 scenarios, and 22 CTF challenges for learning, training, and red team exercises.
AIComply
Inline content classifier for AI agent input and output. Detects PII, credentials, and regulated data before an agent sends it to a cloud LLM.
Leadership
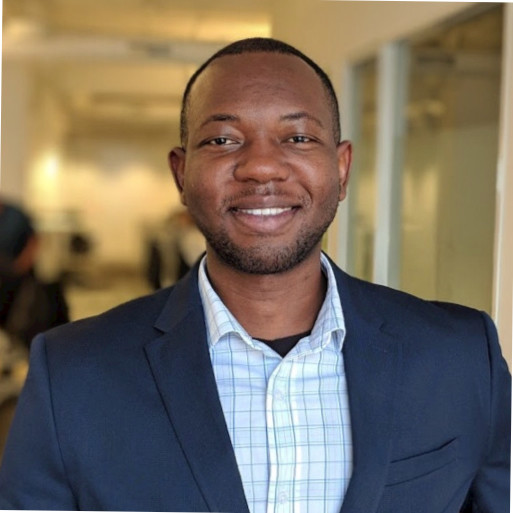
Founder & CEO
Abdel Fane
Founder of OpenA2A. Twenty years securing enterprises. Now securing the agents that are starting to run them.
CEO and Founder, OpenA2A
Executive Director, CyberSecurity NonProfit (CSNP)
Co-Creator, QRAMMQuantum Readiness Assurance Maturity Model
Background
Twenty years of technology and cybersecurity leadership across healthcare, financial services, technology, government, energy, consulting, insurance, and pharmaceuticals.
Masters in Cyber Forensics & Security
Why open source
Security infrastructure should be auditable end to end. Trust does not come from a vendor pitch.
Transparency
The tools' code is public. Audit it, fork it, run it under your own scrutiny.
Community
The best security comes from collective knowledge. We build with the community, not against it.
No lock in
Self host forever. Your security never depends on a vendor business model or a pricing change.
Apache 2.0 on all ten tools.
If you are building AI agents, secure them. If you are deploying them, verify them. If you are auditing them, verify the trail.