Press & Media
Resources for journalists, analysts, and media covering AI security and agent infrastructure.
Demo Video
AIM: Open Source Security Platform for AI Agents and MCP Servers - Full Demo
Walkthrough of AIM: agent registration and Ed25519 identity, MCP server attestation, trust scoring and SDK integration.
Conference recordings and slide decks are collected on the talks page.
FOR IMMEDIATE RELEASE. December 2025. Updated
OpenA2A Launches AIM: Open-Source Identity Management for AI Agents
DENVER, CO. OpenA2A today announced the public launch of AIM (Agent Identity Management), an open-source platform that gives each AI agent its own cryptographic identity and checks the actions the agent submits against the capabilities granted to it. In strict mode AIM refuses an action whose capability was not granted, whatever led the agent to attempt it; in the default mode the action runs and AIM raises an alert.
"AI agents are the new attack surface," said Abdel Fane, Founder and CEO of OpenA2A. "The EchoLeak vulnerability demonstrated that AI agents in production face real security threats. AIM gives each agent a cryptographic identity and applies capability-based access control: it checks the actions an agent submits against the capabilities granted to it, and in strict mode refuses the rest. AIM records the agent actions it verifies."
Key Features
- Registration:
agent = secure("my-agent")registers the agent with an AIM server: the SDK generates the agent's Ed25519 key pair on the machine and registers the public key, and the server gives the agent an initial trust score. It needs credentials for that server first. - MCP Server Attestation: Agents submit signed attestations of the MCP servers they connect to, and the AIM server checks each signature against the agent's registered key. A drift alert is raised when a capability detection run finds that a server's manifest has changed since the last run.
- Connections: A record of the MCP servers agents report connecting to, with their attestation status.
- MCP Asset Management: For each MCP server registered with it, AIM records the user who registered it, the agents that report connecting to it, and the tools, resources and prompts the server declares or that agents report. AIM does not determine what a server can access.
- 9-Factor Trust Scoring: A trust score from nine weighted factors, recalculated on events such as registration, verification by an administrator, capability changes and capability reports from the SDK. A capability violation also lowers the stored score directly, and each action check reads the stored score.
Framework Support
The Python SDK includes integrations for LangChain, CrewAI and MCP, and its decorators wrap any Python function. secure() detects the agent type and likely capabilities from the libraries the agent imports, and by default installs hooks for LangChain, CrewAI, OpenAI and Anthropic that record calls. The hooks allow and block nothing; actions are checked through the SDK's decorators.
Enterprise Supply Chain Security
As AI agents proliferate across enterprises, they create complex dependency chains with MCP servers, external APIs, and other agents. AIM addresses this supply chain risk with challenge verification of MCP servers, run by an administrator, and signed attestations from the agents that connect to them, with event-driven detection of configuration drift. AIM shows a graph of the organization's agents and the MCP servers registered with it, linked by the connections agents report. By default nothing in AIM stops an agent from connecting to a server; with the SDK's optional MCP action wrapper, an agent asks AIM before each MCP action, and AIM refuses the action when the server is not marked verified.
MCP Asset Management
MCP servers give agents access to databases, files and APIs, and an organization may not know which servers its agents use. AIM keeps a record of the MCP servers registered with it: who registered each one, which agents report connecting to it, and the capabilities each declares.
Availability
AIM is available today under the Apache-2.0 open-source license. Organizations can self-host it with Docker Compose or use AIM Cloud, a hosted service built from a private mirror of the AIM repository with cloud-only additions.
About OpenA2A
OpenA2A builds open-source security infrastructure for AI agents. It was founded by Abdel Fane, Executive Director of CSNP.
Media Contact: info@opena2a.org
Changes to this release:
- , corrected the release to match AIM's code.
- Lede: it said one SDK call protects an agent from three kinds of attack. The call registers the agent; AIM checks submitted actions, refuses ungranted ones only in strict mode, and does not detect prompt injection.
- Quote: replaced with words the founder approved; they no longer call audit trails complete.
- Features and sections: an administrator runs MCP verification, connections are as agents report them, server access is not classified, and AutoGen and a compliance sentence were removed.
- Availability: names AIM Cloud's private mirror and drops the licensing forecast.
- About OpenA2A: shortened.
- , removed the feature line about SOC 2, HIPAA and GDPR audit trails.
- , changed the trust scoring feature from eight factors to nine.
- , replaced em dashes with other punctuation, including in the dateline and the founder's quote; no words changed.
- , changed "Real-time behavioral analysis" to "Event-driven behavioral analysis" in the trust scoring feature, and "continuous monitoring for configuration drift" to "event-driven detection of configuration drift" in the supply chain section.
- , changed the founder's name in the quote's attribution and in About OpenA2A to Abdel Fane.
- , removed "for free" from the Availability paragraph; the license did not change.
- , changed the license in the Availability paragraph from AGPL-3.0 to Apache-2.0, on the day AIM's license changed.
Fact Sheet
Key Statistics
- Reported AI breaches
- 74%
- of organizations reported knowing of an AI breach in 2024, in a survey of 250 IT leaders (HiddenLayer AI Threat Landscape Report, 2025)
- EchoLeak severity
- 9.3 Critical
- CVSS 3.1 score of CVE-2025-32711 in Microsoft 365 Copilot, published 2025-06-11. Microsoft had already fully mitigated it.
Tool Information
- Tool Name
- AIM (Agent Identity Management)
- Company
- OpenA2A
- License
- Apache-2.0 (Open Source)
- Languages
- Go, TypeScript, Python, Java
- Cryptography
- Ed25519 Signatures
- Framework Support
- LangChain, CrewAI, MCP
- Deployment
- Self-hosted or AIM Cloud (hosted)
Key Differentiators
- Open-source platform with cryptographic agent identity
- Registration in one call; actions checked through SDK decorators
- MCP server attestation, with drift recorded at the next verification, detection run or attestation consensus
- Supply chain visibility: a graph of agents and the MCP servers they report connecting to
- MCP asset management: a record of registered MCP servers, who registered them and the capabilities they declare
- Trust score from nine weighted factors, read by each action check
Leadership
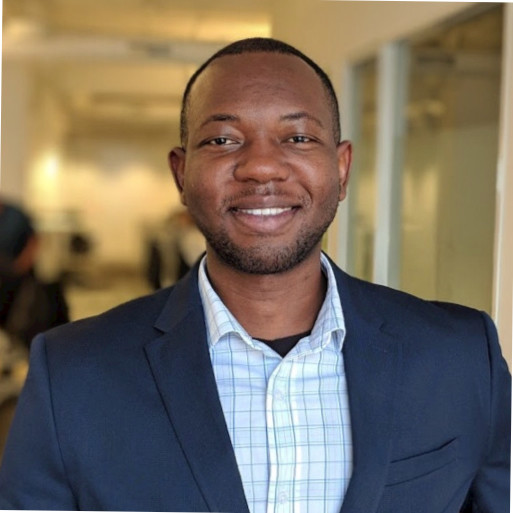
Abdel Fane
Founder & CEO
Executive Director of CSNP
Key Talking Points
On the Problem
- "Traditional security assumes human-in-the-loop. Agents operate autonomously."
- "Every unverified agent is a potential insider threat with API access."
On the Solution
- "Each agent has its own Ed25519 key, and AIM verifies each signed action check against the public key registered for that agent."
- "In strict mode, AIM denies an action whose capability the agent was not granted, and the SDK blocks the call before it runs."
- "Registering an agent takes one call; its actions are checked through the SDK's decorators."
On Supply Chain Security
- "Every MCP server your agent connects to is a potential attack vector."
- "AIM records the MCP servers agents report connecting to, and records a change to a server's declared tools when an administrator verifies the server, a member runs detection, or agents' attestations reach consensus."
On MCP Asset Management
- "An organization may not know which MCP servers its engineers run or its agents use."
- "AIM keeps a record of the MCP servers registered with it: who registered each one, which agents report connecting to it, and the capabilities each declares."
On Timing
- "EchoLeak (CVE-2025-32711) showed this isn't theoretical: a critical vulnerability in a production AI assistant, mitigated by Microsoft before the CVE was published in June 2025."
- "AIM's source is on GitHub under Apache-2.0 because trust requires transparency. The hosted AIM Cloud is built from a private mirror with cloud-only additions."